

Bitcoin cost processor BTCPay Server has warned that bots are probing uncovered Lightning nodes for a possible path to administrative management.
The exercise follows a separate essential BTCPay vulnerability that attackers exploited a month in the past to acquire credentials defending LND nodes and drain service provider wallets.
BTCPay subsequently disabled exterior entry to LND, a broadly used implementation of Bitcoin’s Lightning Community, in its customary Docker deployment. The mission now says automated programs are concentrating on servers the place operators manually restored that entry, repeatedly calling an LND password-change endpoint.
Bitcoin Core Lightning Docker bug leaves node operators uncovered regardless of displaying up to date model
The most recent mechanism differs from the vulnerability exploited in August however may result in the same final result: an attacker acquiring credentials that may management an LND node.
BTCPay stated the opening seems throughout a brief interval after LND restarts, whereas its pockets stays locked. Throughout that interval, the focused password-change technique doesn’t require a macaroon, the credential LND usually makes use of to authorize administrative actions.
Older BTCPay LND wallets compounded the danger by utilizing a shared default password. An attacker who may attain the interface earlier than BTCPay’s inner unlocker may doubtlessly submit that password first, exchange it, and request an administrator macaroon that offers management over the node.
BTCPay has not reported a profitable takeover by means of the newly noticed exercise or linked the bots to the attackers behind the August thefts.
BTCPay hardens nodes after August theft
The renewed probing extends a tough safety stretch for BTCPay, which acknowledged on Aug. 7 that attackers had exploited a vulnerability affecting all variations earlier than 2.4.2. That flaw allowed unauthenticated attackers to acquire LND macaroon information and use them to maneuver funds. BTCPay’s customary on-chain wallets had been unaffected.
Days later, the mission and its supporters provided a bounty equal to 10% of recovered bitcoin, capped at 3 BTC, then value about $190,000. BTCPay additionally enlisted exchanges, blockchain analytics companies, and legislation enforcement in efforts to hint the stolen funds.
Model 2.4.4, launched Sept. 7, now addresses the circumstances behind the newest assault path. New LND wallets obtain distinctive random passwords, whereas older installations utilizing the shared credential are migrated and have their passwords rotated.
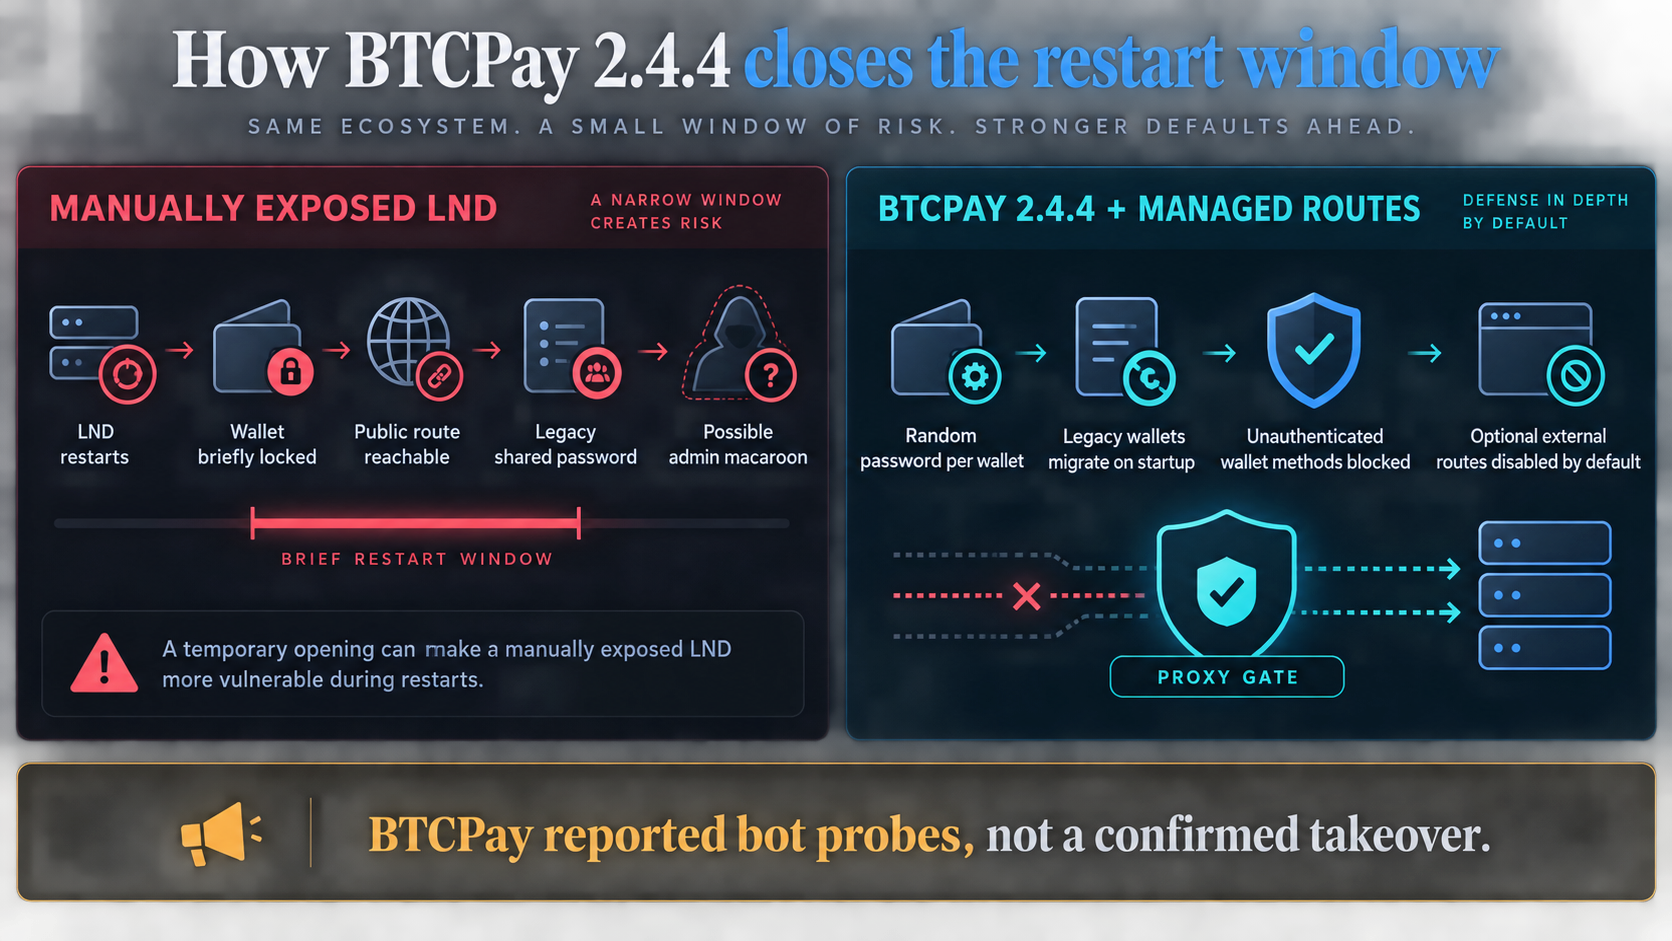
BTCPay’s customary reverse proxy additionally blocks unauthenticated pockets setup and unlock strategies, closing the restart-time opening by means of its managed public community path.
These controls can’t safe infrastructure operators configure independently. Directors who created their very own reverse proxy or in any other case uncovered LND publicly can nonetheless bypass BTCPay’s protections.
BTCPay has urged directors to put in model 2.4.4 and take away manually uncovered LND routes. A route-control change merged Sept. 11 gives a supported choice for distant entry whereas protecting LND and Core Lightning interfaces disabled by default.
That leaves customized deployments because the instant concern. Operators utilizing them should audit their proxy guidelines and migrate distant connections behind BTCPay’s managed controls whereas automated programs proceed looking for reachable nodes.