

On September 6, 2026, Liquid’s federation launched roughly 3,996 BTC after its community accepted L-BTC that lacked Bitcoin backing. Liquid is a Bitcoin sidechain whose L-BTC is supposed to characterize bitcoin held in a federation reserve. A validly licensed withdrawal turned the invalid sidechain state into an actual Bitcoin fee price about $320 million on the time. A payout restrict earlier than federation signing might need interrupted that exit.
Alpen Labs CEO Simanta Gautam now says his AI brokers traced the flaw and reproduced it regionally in about an hour. The work started after he heard of the September 6 assault. His September 22 account and technical report give an in depth clarification of the failed proof test. The demonstration got here after the funds left, so its pace says little by itself about whether or not a standing AI monitor would have raised an actionable warning earlier than the assault.
Components, the software program underlying Liquid, caches profitable checks of the cryptographic proofs hooked up to confidential transactions. A September 1 code change tried to make every cached consequence depend upon all of the context that impacts verification, together with the asset generator and output script. Alpen says the change concatenated these fields as uncooked bytes with out encoding their boundaries. A sound “seed” proof and a unique, invalid goal may subsequently produce similar cache enter.
In Alpen’s native replay, recent verification rejected the goal, whereas the affected cache wrapper accepted it after the seed had populated the cache. A profitable cache lookup bypassed the proof test that ought to have rejected the goal. The 2 statements had the identical enter bytes for the cache regardless that they represented completely different verification requests. This was a neighborhood replica of the suspected consensus failure. Alpen says precise manufacturing validator binaries and historic cache contents have been unavailable, leaving the deployed code and reside priming path strongly inferred from the supply and chain proof.
SideSwap says a personal safety construct put in by itself node in August accepted the assault transaction. That account narrows the deployment query for one operator however doesn’t determine each federation functionary’s construct. On September 8, an Components restore modified cache keys to encode discipline lengths, added collision-focused exams and launched an choice to bypass the range-proof cache. Model 23.3.4 adopted on September 9. These adjustments tackle the validation gate earlier than invalid L-BTC can grow to be accepted state.
The licensed exit nonetheless wanted a separate test
In response to SideSwap’s account, the attacker despatched 4,000 L-BTC to its peg-out service at 14:05 UTC on September 6. SideSwap burned the tokens with legitimate authorization at 14:06. The order exceeded its personal pockets funds, inflicting two tried payouts to fail earlier than federation signers launched 3,996 BTC at 14:28. SideSwap says it forwarded 3,995.99999857 BTC to the client’s tackle in the identical Bitcoin block.
The accepted order exhibits why a sound key was inadequate as a security test. SideSwap says its authorization key was on-line, payouts have been automated, and its service had no dimension, velocity, supply-relative, wallet-history or human-review checks. The federation additionally signed an distinctive request after the 2 failed makes an attempt. A payout restrict or different impartial maintain on the service or federation, utilized earlier than authorization or signing, may have stopped this specific payout path even after Liquid admitted invalid state.
An offline authorization key would have created a pause earlier than SideSwap authorised the peg-out. A delayed handbook ahead would have acted later. It may have left the Bitcoin paid by the federation beneath SideSwap’s management for return, however the federation’s reserve switch would have already got occurred. The exact place a safeguard acts determines which loss it may well stop.
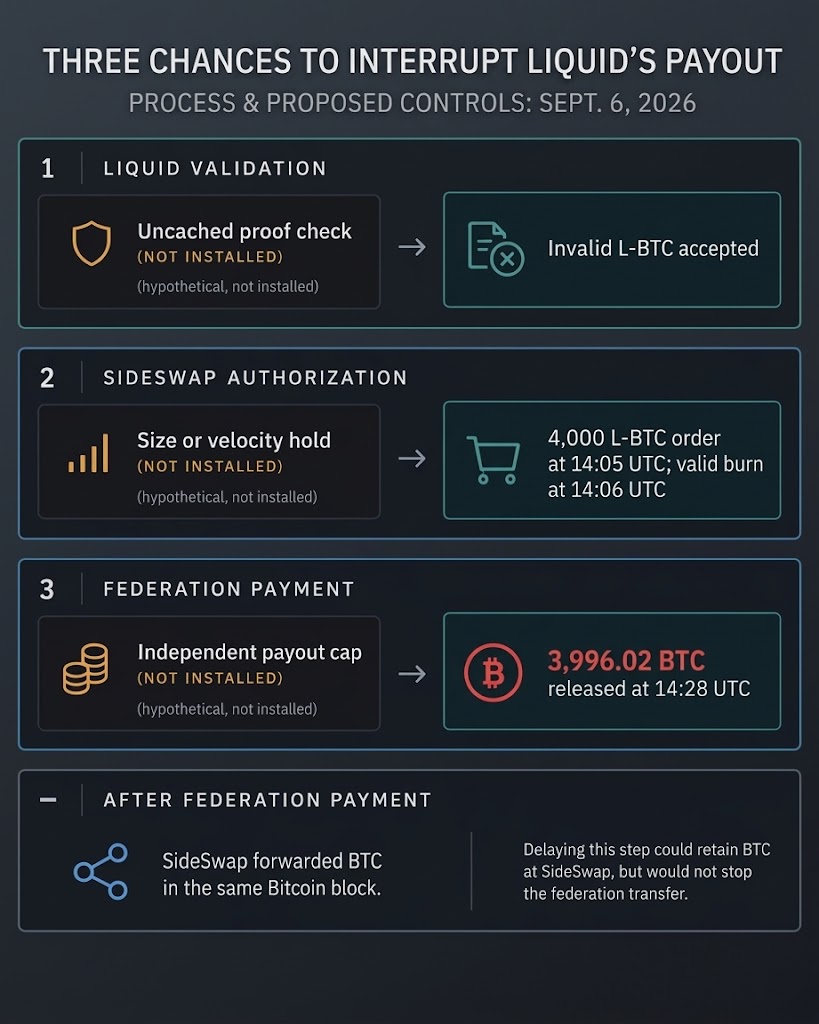
Gautam’s one-hour consequence describes a retrospective investigation. The native replay demonstrates how the cache may return the unsuitable reply beneath the assessed code; it doesn’t measure a steady detector’s likelihood of discovering the defect earlier than deployment or present a document of the precise manufacturing cache state. A corrected validator may reject the invalid sidechain transaction. A payout restrict may comprise losses if one other defect nonetheless reaches the bridge. The controls tackle completely different failures.
Liquid stated on September 17 that strange transactions had resumed whereas peg-outs remained paused. It stated withdrawals would restart solely after full one-to-one BTC backing was confirmed and required software program updates, testing and impartial opinions have been full. The unanswered operational query is whether or not the resumed peg may have an impartial cause to cease a reserve-sized licensed request earlier than Bitcoin leaves federation custody.