

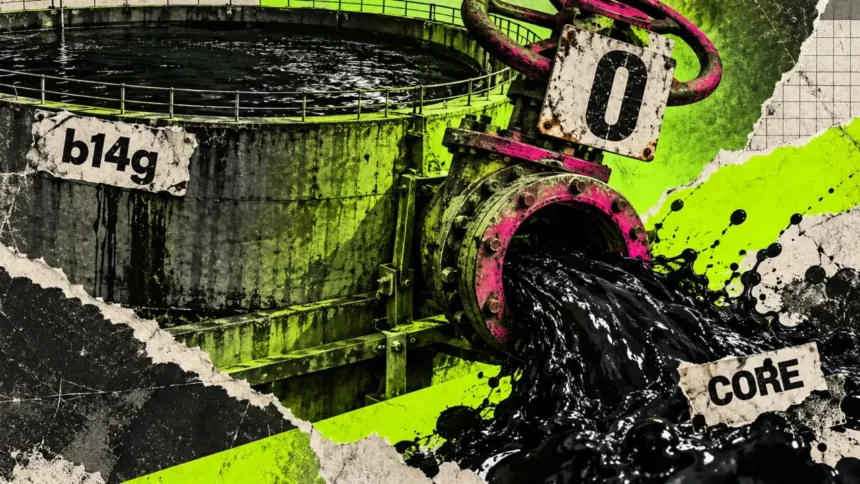
Bitcoin staking platform b14g suffered a $1.47 million exploit on Oct. 31, shedding roughly 97 million CORE tokens.
The attacker drained 91 staking positions in a single transaction by submitting withdrawal requests for zero CORE, in keeping with an investigation by blockchain analytics agency Bitquery.
The staking platform confirmed the unauthorized withdrawals and stated it had paused the affected contracts whereas coordinating with the Core workforce, safety companions, and exchanges to recuperate the funds.
Nevertheless, b14g clarified that the breach was restricted to CORE deposits. Bitcoin staked by the protocol stays time-locked on the BTC blockchain and was not affected.
How hackers exploited b14g’s withdrawal mechanism
Bitquery’s investigation revealed that the attacker exploited a weak point within the interplay between b14g’s withdrawal mechanism and Core’s staking contracts.
Underneath regular circumstances, b14g permits Bitcoin holders to pair their BTC with CORE deposits to earn enhanced staking rewards. The protocol manages these preparations by staking positions that maintain CORE and delegate it to validators.
Nevertheless, Core’s staking contract comprises an uncommon provision that interprets a withdrawal request for zero tokens as an instruction to withdraw your complete staked stability.
The attacker exploited this habits by submitting 99 zero-value withdrawal requests in opposition to staking positions it had not funded.
Fairly than rejecting the unauthorized requests, b14g’s contract accepted them and handed the directions to Core’s staking system, which launched roughly 97 million tokens.
Bitquery stated the exploit occurred at 09:29 UTC, with the stolen tokens transferred to an attacker-controlled pockets.
The investigation discovered no proof that the attacker wanted a compromised administrator key or a newly deployed malicious contract. As a substitute, the underlying contract logic had reportedly been in place for roughly 17 months.
Nevertheless, Bitquery cautioned that it had not reviewed b14g’s underlying supply code and couldn’t establish the exact programming error that allowed the unauthorized withdrawals.
In the meantime, blockchain information confirmed that b14g didn’t pause the affected contracts till 10:35 UTC, roughly 66 minutes after the preliminary assault.
Throughout that interval, the attacker transferred 23 million CORE from the unique pockets by a number of newly created addresses.
The timeline doesn’t set up when b14g found the breach, though the platform stated it paused the contracts instantly after figuring out the incident.
Additional tracing revealed that some stolen funds moved by middleman addresses linked to change infrastructure related to Bybit, Gate.io, and MEXC.
Bitquery additionally recognized a service that equipped the attacker’s preliminary transaction charges, then obtained about 11 million CORE from the stolen funds and forwarded them to an MEXC deposit handle.
Nevertheless, the analytics agency cautioned that some middleman wallets additionally dealt with different clients’ belongings, making it tough to attribute each subsequent switch on to the attacker.
By the night of Oct. 31, roughly 68 million CORE, representing 70% of the stolen tokens, had remained unmoved in three wallets.
Individually, b14g reported that change companions had frozen roughly 9 million CORE linked to the attacker.
In its response, Core DAO maintained that the underlying blockchain had not been compromised, stressing that its consensus mechanism, validators, and staking contracts continued working usually all through the incident.
It additionally stated CORE staked straight with validators or by different protocols remained unaffected.
b14g has pledged to publish an in depth autopsy explaining the technical reason behind the exploit, the extent of person losses, and the following steps for affected depositors. The platform has not but disclosed a compensation plan.