

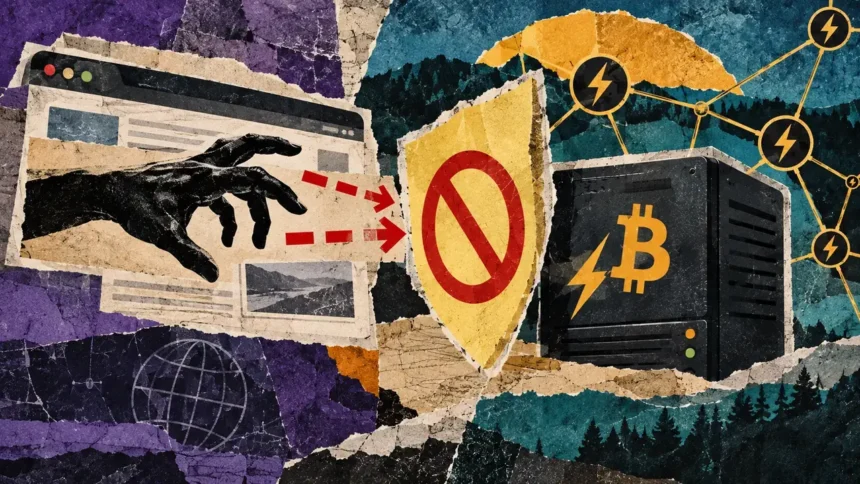
Eclair, ACINQ’s Bitcoin Lightning node software program, launched v0.14.4 on Oct. 15 to dam malicious webpages from issuing authenticated node instructions via an operator’s browser.
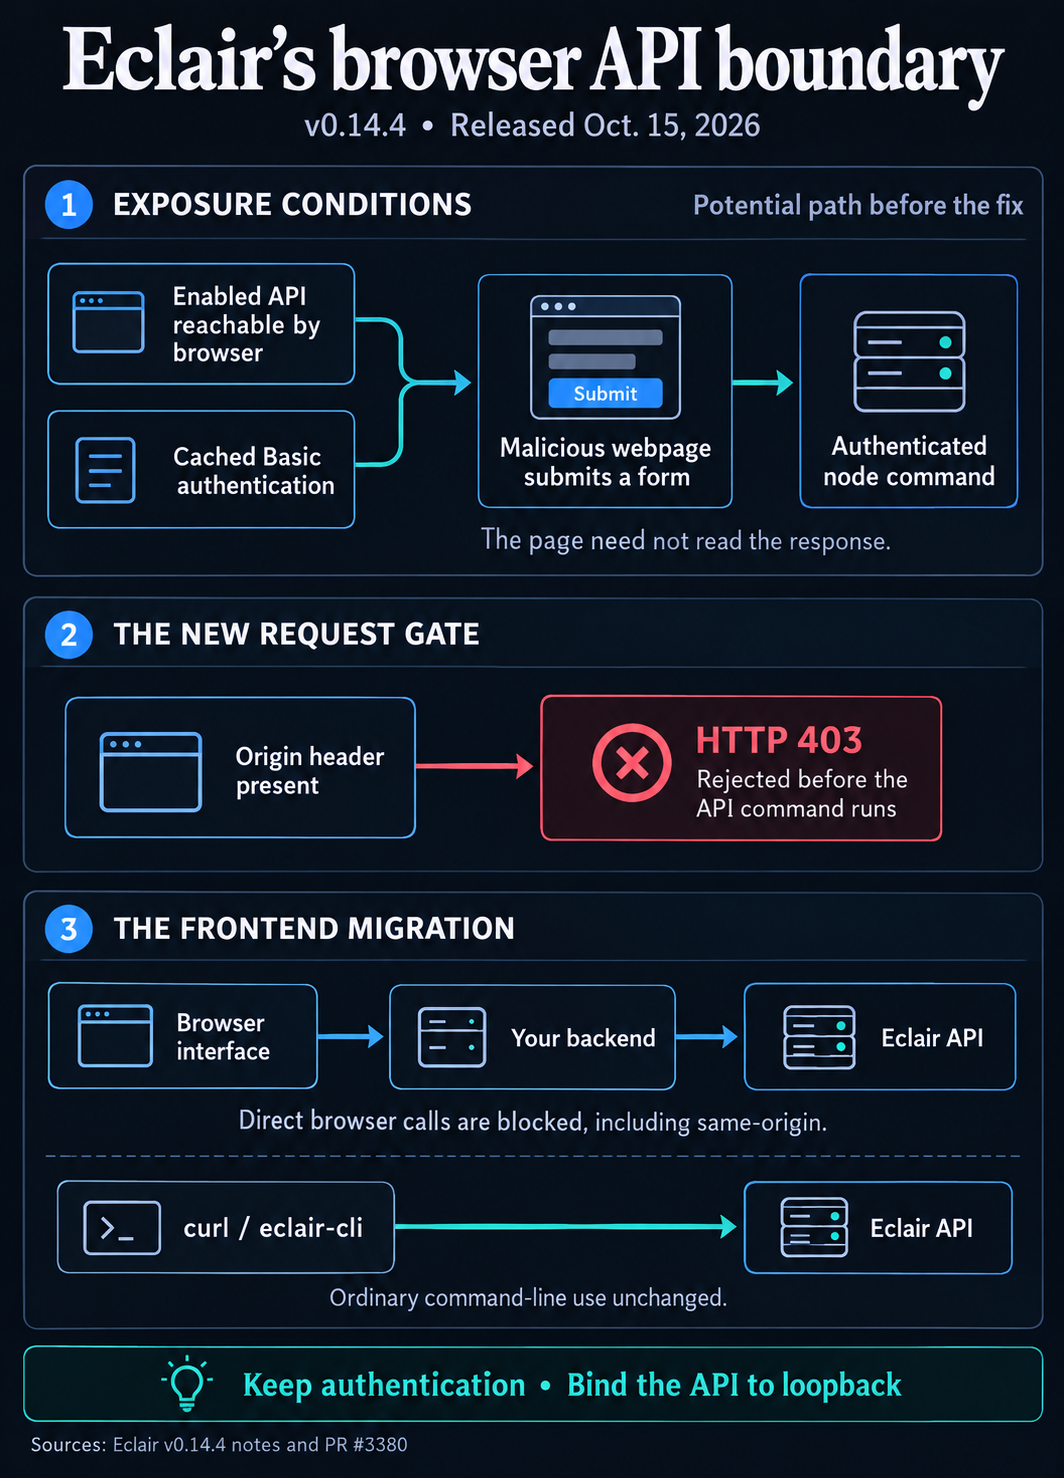
The publicity will depend on an enabled Eclair API that the operator’s browser can attain, with HTTP Primary authentication already cached in that browser. Eclair’s node API can learn node state, open and shut channels, and ship and obtain funds.
Eclair’s v0.14.4 launch notes clarify how cached authentication lets a malicious webpage submit a plain HTML kind to the node’s API. The browser attaches the saved credentials routinely. The attacker can not learn the response, however the authenticated command nonetheless reaches the node.
Browser interfaces want a backend
The patch returns HTTP 403 earlier than the API route runs each time a request carries an Origin header, no matter its worth.
The restriction additionally impacts official browser interfaces, together with these hosted on the identical origin because the API. These frontends now want an middleman backend between the browser and Eclair.
Unusual command-line entry continues. The maintainers say curl and eclair-cli don’t ship the Origin header, so their regular API requests are unaffected.
The Origin test nonetheless leaves authentication and community restrictions important. A non-browser shopper can omit the header, so its absence doesn’t set up {that a} request is allowed. Eclair maintainer pm47 says the API ought to stay certain to loopback, proscribing community entry to the native machine.
The browser repair merged on Sept. 15 in pull request #3380 and is included in v0.14.4 alongside the funding-fee and signer repairs mycryptopot lined on Oct. 12.
Maintainers advocate upgrading and say operators can cease Eclair, set up the replace and restart with out closing their Lightning channels.